Coverage note
Citrix penetration testing for remote access estates
Citrix penetration testing examines the remote access layer many organisations depend on. So it checks gateways, published applications and whether a session stays inside its boundaries.
- Manual exploit chains
- PTES and the OWASP testing guide
- Authorised scope only
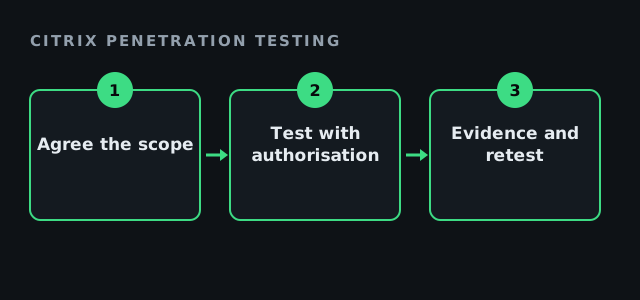
Why citrix penetration testing matters
Remote access gateways face the internet by design. Therefore they attract attention whenever new weaknesses are announced, and patching must keep pace.
Inside the session, users reach business applications. Also, a published application can sometimes reveal more of the desktop than intended.
What citrix penetration testing covers
The test covers the path from the internet to the session and beyond. For example, whether a user can leave a published application.
- Gateway configuration and patch level
- Authentication and multi-factor setup
- Published application boundaries
- Session policies, such as clipboard and drive mapping
- Network reach from inside a session
Citrix penetration testing readiness check
Tick what is already true. Open items go into the written rules of engagement.
Your result appears here as you tick, so you can see what is still open.
Scoping citrix penetration testing
Estate size drives effort. However, user roles matter as much as server counts.
| Question | Effect on scope |
|---|---|
| How many gateways? | Each is reviewed |
| How many published apps? | Boundaries checked per app |
| Which user roles? | Each role adds checks |
| Cloud or on-premises? | Hosting rules apply |
Authorisation and safety
Testing runs only under written rules of engagement. Also, testing windows avoid peak hours, because remote access is business-critical.
In addition, test accounts are created for each role. As a result, no real user session is touched.
Evidence, fees and retest
Findings come with evidence and a fix, following NIST SP 800-115.
Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Attack Surface Diagnostic starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days.
Also plan for urgent patches. Because gateway weaknesses are often announced suddenly, a tested emergency patch process matters as much as the test itself. So agree who can patch out of hours, and how quickly. In addition, review gateway logs after each announcement, because early signs of probing appear there first.
Citrix penetration testing questions
Does Citrix penetration testing include the gateway?
Yes. The gateway is usually the first part of the scope.
Can Citrix penetration testing disrupt users?
Windows and limits are agreed to avoid it.
What does Citrix penetration testing usually find?
Weak session boundaries and gaps in patching or authentication.
Who leads the work?
A senior penetration hacker.
Related guides
Send the brief for citrix penetration testing
Describe your remote access estate and user roles. The penetration hacker who would lead the work replies with a written scope and one fixed fee.
Send the brief