Coverage note
VoIP penetration testing for business phone systems
VoIP penetration testing checks the systems behind your business telephony. So it covers call servers, admin access, trunks and how voice traffic is separated from the rest of the network.
- Manual exploit chains
- PTES and the OWASP testing guide
- Authorised scope only
Why voip penetration testing matters
Phone systems run on the same networks as everything else now. Therefore a weak call server can become a foothold, and toll fraud can cost real money quickly.
Telephony is often managed by a separate team or provider. Also, admin portals for phone systems are easy to forget during wider testing.
What voip penetration testing covers
The test covers the platform and its surroundings. For example, whether a desk phone network can reach business servers.
- Call server and admin portal security
- Trunk and provider connections
- Voice network separation
- Voicemail and user portal access
- Logging and fraud monitoring
Voip penetration testing readiness check
Tick what is already true. Open items go into the written rules of engagement.
Your result appears here as you tick, so you can see what is still open.
Scoping voip penetration testing
Platform type drives scope. However, provider agreements may set limits.
| Question | Effect on scope |
|---|---|
| On-premises or hosted? | Hosted platforms limit scope |
| How many sites? | Each site's network is checked |
| Contact centre in scope? | Adds systems |
| Provider involved? | Their rules apply |
Authorisation and safety
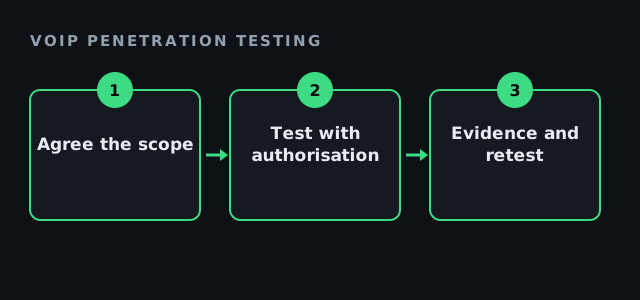
Testing runs only under written rules of engagement, and the provider's terms are checked first. Also, testing never disrupts emergency calling.
In addition, no calls are placed to outside numbers without agreement. As a result, nothing affects customers or costs.
Evidence, fees and retest
Findings come with evidence and a fix, following NIST SP 800-115.
Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Attack Surface Diagnostic starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days.
Also review provider access. Because many phone systems are supported remotely by a provider, their access path deserves the same scrutiny as your own. So confirm how they connect and who approves it. In addition, set spending alerts on trunks, because fraud shows up quickly in call costs.
Voip penetration testing questions
Does VoIP penetration testing affect calls?
It is planned to avoid disruption, and emergency calling is never touched.
Can VoIP penetration testing cover a hosted platform?
Your configuration and portals, within the provider's terms.
What does VoIP penetration testing usually find?
Weak admin access and poor separation of voice networks.
Who leads the work?
A senior penetration hacker.
Related guides
Send the brief for voip penetration testing
Describe your phone platform and sites. The penetration hacker who would lead the work replies with a written scope and one fixed fee.
Send the brief