Coverage note
DevOps penetration testing: the pipeline as an attack surface
DevOps penetration testing looks at the systems that build and ship your software. So it covers runners, artefact stores and secrets handling, because that is where modern breaches increasingly start.
- Manual exploit chains
- PTES and the OWASP testing guide
- Authorised scope only
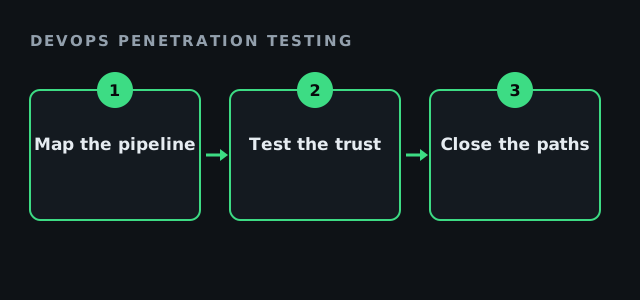
Why DevOps penetration testing matters
A pipeline holds keys to almost everything it deploys. Therefore a weakness there can reach production without touching the application itself. As a result, a clean application test can still leave the route wide open.
What DevOps penetration testing covers
Scope is agreed in writing first, and then shaped around how your team actually ships.
- Build runners and the permissions they hold
- Artefact stores and package registries
- Secrets handling, rotation and exposure in logs
- The trust between source control, the pipeline and the cloud
| Surface | The question | Evidence returned |
|---|---|---|
| Runners | What can a job reach? | The permissions actually used. |
| Secrets | Where do they leak? | Each exposure, with its location. |
| Registries | Who can publish? | The write paths found. |
Scope your DevOps penetration testing
Tick what applies. Each tick usually adds a surface to the written scope.
Your result appears here as you tick, so you can see what is still open.
How DevOps penetration testing stays safe
Pipelines are live systems, so care matters. For example, testing windows avoid release days, and nothing is pushed to production. In addition, any credential observed during testing is reported for rotation. Then every artefact we placed is removed at close.
What the DevOps report shows
Findings come back as reproducible chains, with the request, the response and the artefact at each step. So your engineers can verify each one without guessing. Also, each fix is ranked by how much of the chain it breaks. Our method follows the Penetration Testing Execution Standard.
Fees for DevOps penetration testing
Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Attack Surface Diagnostic starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days. One fixed number is agreed after a written technical brief, so there are no change orders mid-project.
DevOps penetration testing questions
Is DevOps penetration testing different from an application test?
Yes. It tests how software is built and shipped, not the running application itself.
Does DevOps penetration testing need source code access?
Not always. However, read access to pipeline definitions usually makes the work faster and deeper.
Can DevOps penetration testing break a release?
Testing windows avoid release days, and nothing is pushed to production.
Who authorises testing of a hosted service?
You authorise your own configuration. Also, the provider's testing policy is checked in the scope.
Related guides
Send a DevOps technical brief
Describe how your software is built and deployed. The penetration hacker who would lead the work replies with a written scope and one fixed fee.
Send the brief