Coverage note
IoT penetration testing: the device, the app and the cloud together
IoT penetration testing treats a connected product as one system. So the device, the companion app and the cloud service behind it are tested together, because a weakness in one is often reached through another.
- Manual exploit chains
- PTES and the OWASP testing guide
- Authorised scope only
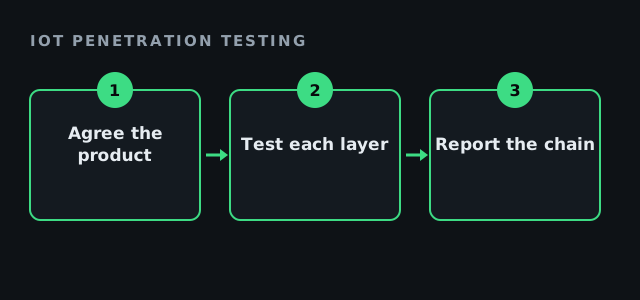
What IoT penetration testing covers
Connected products have more surfaces than a web application. Therefore the scope is agreed layer by layer, with the OWASP Internet of Things project as a common reference.
- The device, its interfaces and its update process
- The companion mobile or web application
- The cloud service and its device identity
- How data moves between all three
Who IoT penetration testing suits
It suits manufacturers before a launch, and buyers assessing a product before rollout. In both cases, however, the right to test must be clear first.
| Situation | Who authorises | Typical scope |
|---|---|---|
| Your own product | You, as manufacturer. | Device, app and cloud. |
| A product you deploy | You, plus the vendor terms. | Your deployment and configuration. |
| A fleet already in use | You, as operator. | Agreed sample devices. |
Ready for IoT penetration testing?
Tick what you can provide. Gaps are settled in the written scope.
Your result appears here as you tick, so you can see what is still open.
How IoT penetration testing stays safe
Devices can be fragile, so testing uses agreed sample units rather than live customer devices. In addition, the cloud tests run inside agreed windows. Also, any device data collected is destroyed when the engagement closes.
What the IoT report delivers
Findings arrive as reproducible chains across layers, with evidence at each step. So your firmware, app and cloud teams each see their part of the fix. Also, the retest is included once the changes ship. Our method follows the Penetration Testing Execution Standard.
Fees for IoT penetration testing
Full engagements run from $35,000 to $120,000, while the floor is $25,000. Also, the bounded Attack Surface Diagnostic starts at $4,500. Moreover, its fee is credited in full against a full engagement commissioned within ninety days. The number is fixed after a written technical brief that lists each layer in scope.
IoT penetration testing questions
Does IoT penetration testing need physical devices?
Usually, yes. Sample units are supplied and returned or wiped at the end.
Can IoT penetration testing use our staging cloud?
Yes, and it is often the safer choice for the cloud layer.
Is a product already on sale testable?
Yes, on units and services you own, with the scope signed first.
Who sees the device findings?
Only the people named in the scope. Findings are destroyed at close.
Related guides
Brief us on the product
Describe the device, the app and the cloud service behind it. The penetration hacker who would lead the work replies with a written scope and one fixed fee.
Send the brief